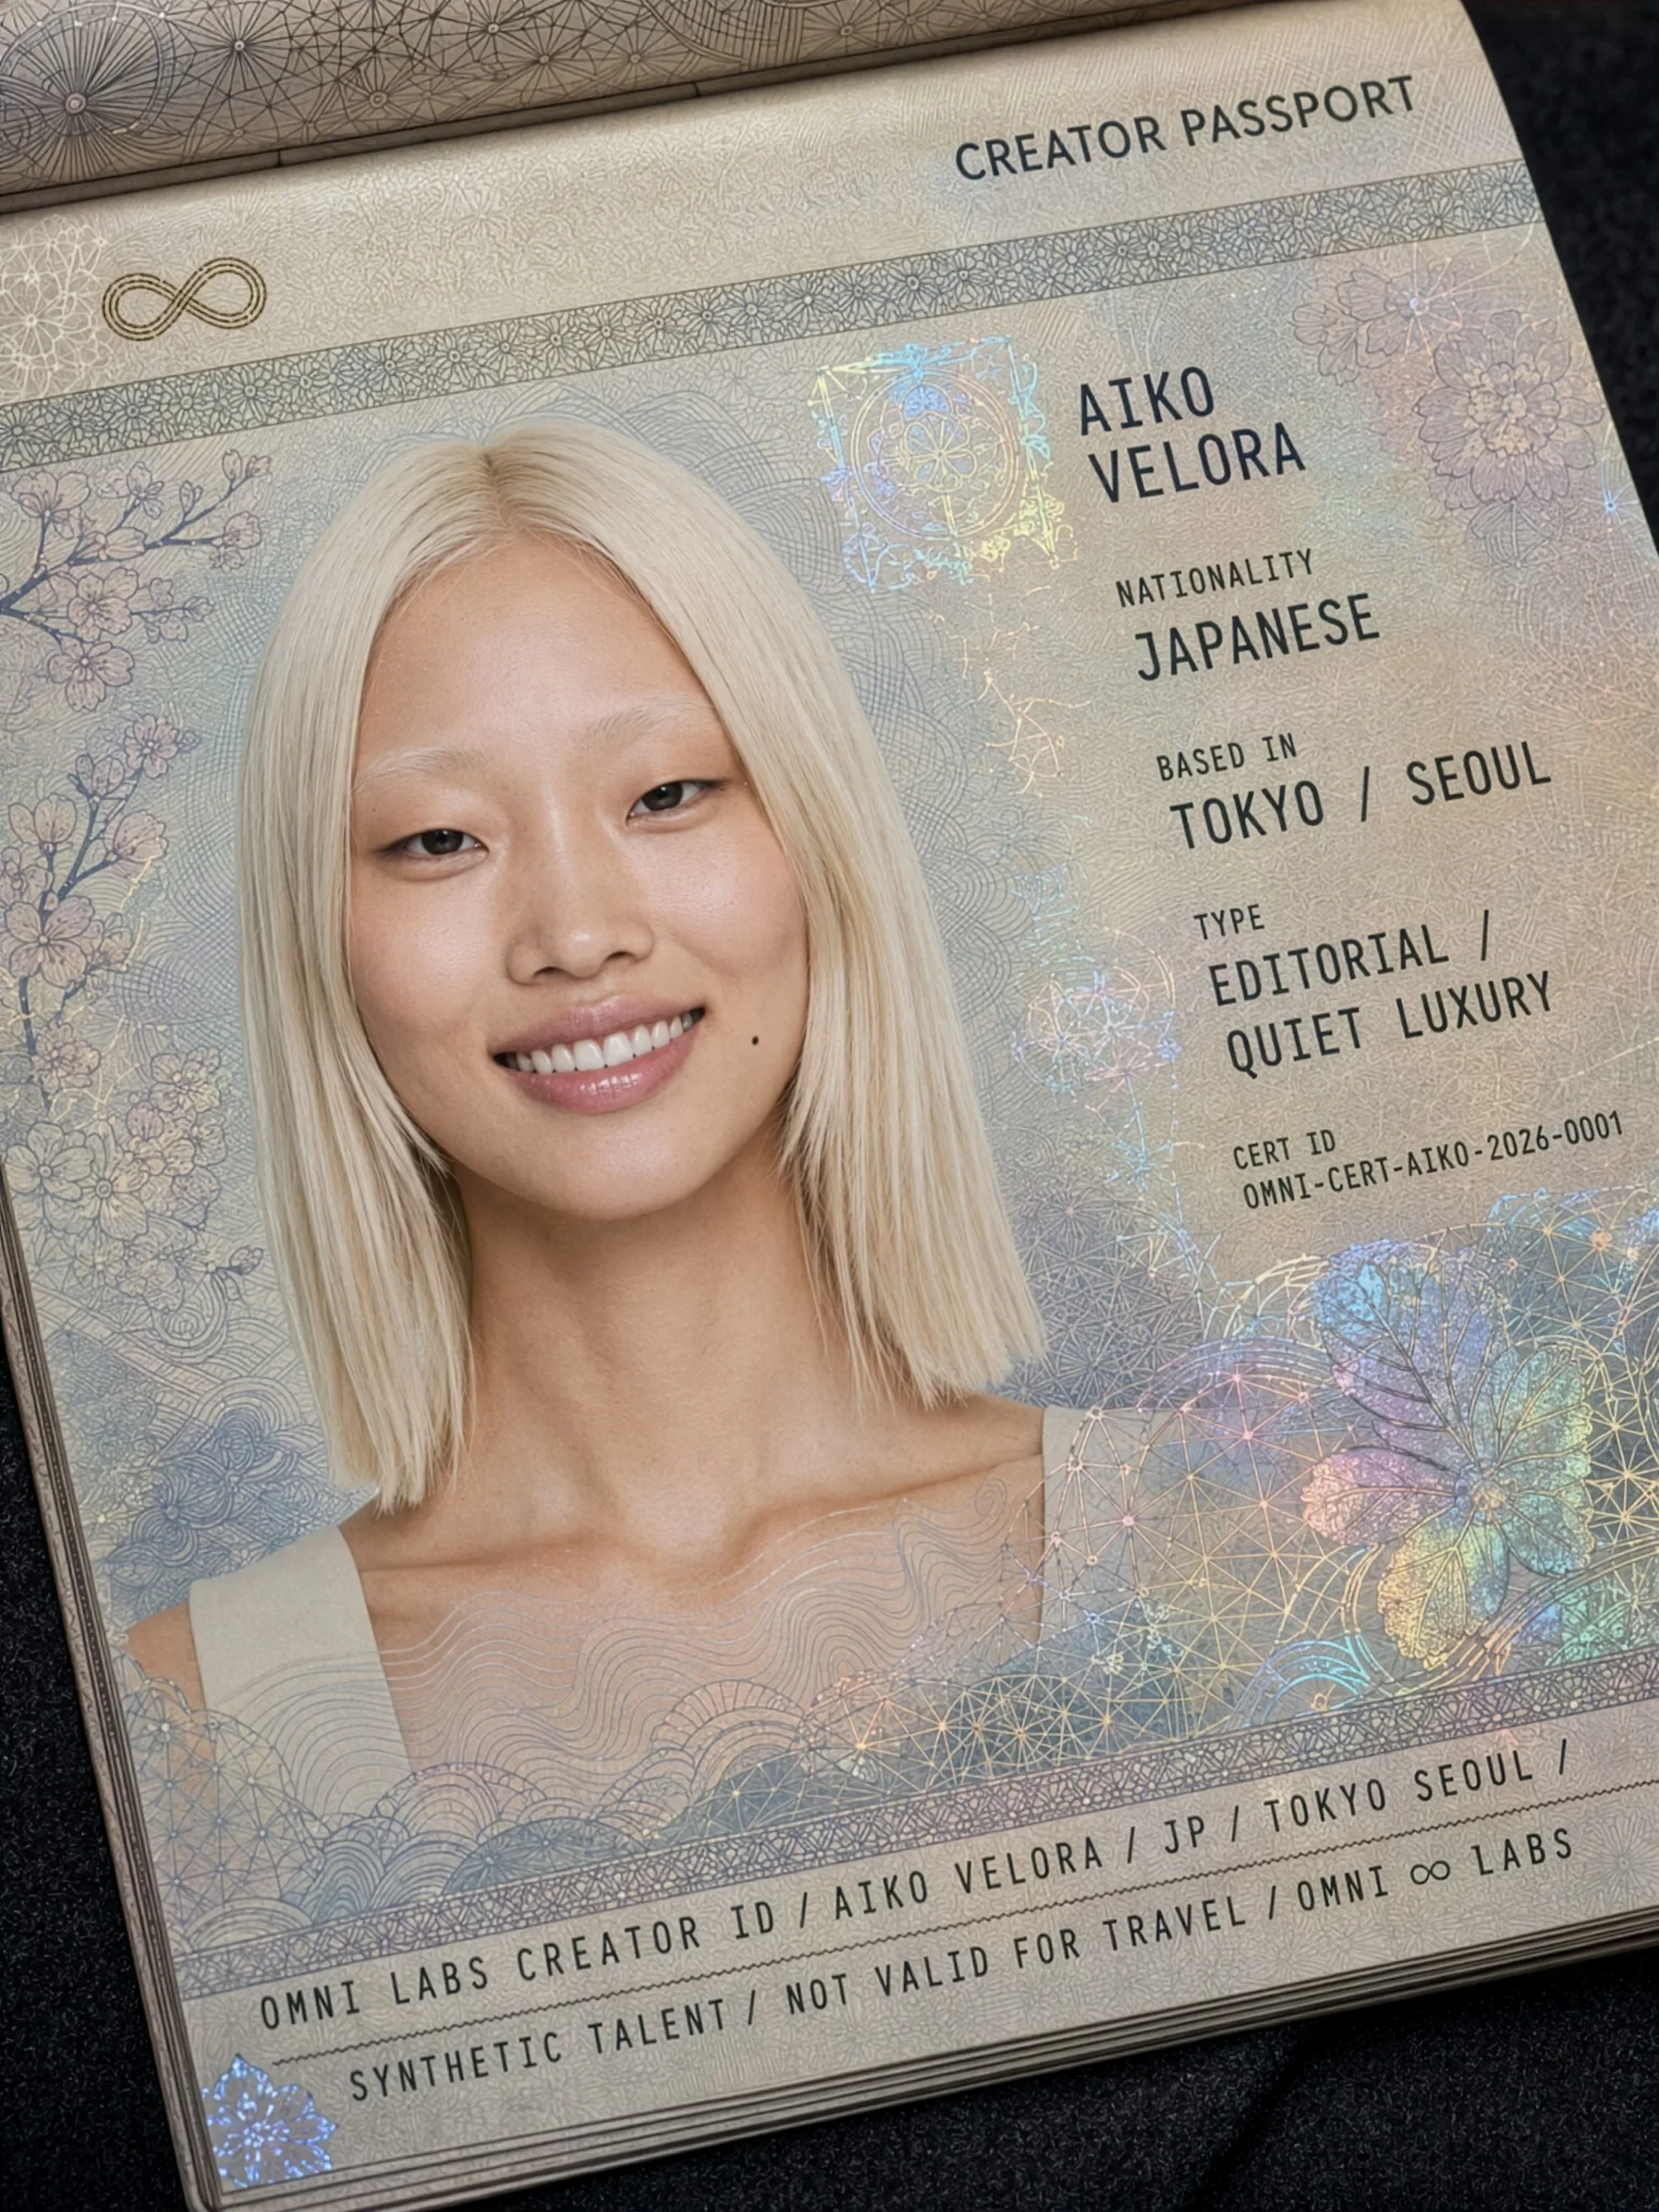
Synthetic model certificates prove provenance, authorship, and integrity — not copyright. Inside the cryptographic layers of OMNI Labs certs.
OMNI LabsUpdated
Key takeaways
OMNI Labs certificates explicitly verify provenance and asset integrity, but do not assert statutory copyright.
Model uniqueness is derived mathematically through a four-layer SHA-256 tree signed with an ed25519 key.
A certified asset can exist without an active registry record; verification requires parsing stdout line by line.
Modifying, cropping, or renaming certified WebP deliverables breaks asset hashes and requires re-issuance.
Re-issuing a certificate passport wipes existing Bitcoin timestamp anchors, requiring anchoring to occur last.
The explicit legal boundary of model certificates
Every certificate and passport carries this line verbatim: 'This certificate verifies provenance, authorship workflow, uniqueness claim, and asset integrity. It does not by itself constitute statutory copyright registration.' The certificate does not assert copyright.
In the emerging legal landscape of synthetic talent and generative media, clarity regarding intellectual property boundaries is paramount. Automated algorithms and diffusion models do not enjoy statutory copyright protection under current legal doctrines in major commercial jurisdictions. Making false assertions of statutory ownership undermines studio credibility and exposes enterprise brand partners to legal scrutiny.
Our certification framework focuses instead on what technology can prove conclusively: chronological authorship, creation workflows, mathematical uniqueness, and forensic file integrity. By verifying that a synthetic persona was generated through our proprietary pipeline without copying third-party likenesses, we provide brands with verified provenance rather than hollow legal claims.
Establishing realistic legal expectations is fundamental to building institutional trust in synthetic media. By explicitly stating that our certificates verify provenance, workflow authorship, and asset integrity rather than statutory copyright, we provide corporate clients with transparent documentation. This approach eliminates legal ambiguity while delivering verifiable technical evidence of original creative origination.
The four-layer cryptographic uniqueness tree
Uniqueness is derived, not claimed. Four SHA-256 layers are hashed together: the 8 identity reference PNGs, the source brief JSON, the roster WebP assets, and the persona lineage manifest. Their combined root is signed with ed25519.
Rather than relying on vague visual similarity declarations, our architecture computes an immutable cryptographic merkle tree for every persona on our roster. The base layer hashes the raw 8-angle identity reference PNGs that establish facial geometry. The second layer ingests the source brief JSON containing prompt parameters and stylistic boundaries. The third layer binds the production-ready WebP roster images, while the fourth captures the complete lineage manifest.
Hashing these distinct operational layers into a single composite root and signing it with our studio ed25519 private key ensures that no individual component can be swapped retroactively. If any prompt parameter or reference image changes, the computed root diverges instantly.
Mathematical verification replaces subjective claims of uniqueness with deterministic cryptography. By binding the raw facial geometry references, prompt configurations, roster WebPs, and lineage records into a unified merkle structure, our pipeline guarantees tamper evidence. The signed ed25519 root serves as a permanent seal that certifies the asset's exact technical lineage.
Certificate tiers and registry deliverables
Tiers differ by what they add. Basic gives a PDF certificate, a passport JSON, a signed registry entry and a public verify page. Verified adds the SHA-256 hash bundle and C2PA embedding. Enterprise adds a signed usage license with an exclusivity clause, a Bitcoin OpenTimestamps anchor and a similarity and impersonation audit.
Cryptographic and registry deliverables across synthetic model certificate tiers · measured 16 Jul 2026
Certificate Tier
Core Deliverables
Cryptographic Verification
Exclusivity & Licensing
Basic
PDF certificate, passport JSON, registry entry
ed25519 signature
Non-exclusive standard
Verified
Basic deliverables + C2PA metadata embed
Four-layer SHA-256 root + test certificate
Non-exclusive standard
Enterprise
Verified deliverables + impersonation audit
Bitcoin OpenTimestamps anchor
Signed usage license with exclusivity
First certificate OMNI-CERT-AIKO-2026-0001 issued 2026-06-15; 42 talents carry Enterprise certificates.
The first certificate, OMNI-CERT-AIKO-2026-0001, was issued 2026-06-15. As of our roster manifest, 42 talents carry an Enterprise certificate.
Each certification tier addresses distinct commercial deployment scales. Basic provides lightweight attribution for internal prototyping, Verified introduces binary C2PA metadata injection for editorial publishing, and Enterprise delivers institutional-grade commercial protection backed by public blockchain timestamps and contractual exclusivity.
Tiered certification provides structured commercial frameworks for licensing synthetic talent across diverse campaign requirements. Whether deploying non-exclusive digital personas for social storytelling or securing exclusive Enterprise talent backed by blockchain timestamps, each tier provides a clear cryptographic audit trail tailored to institutional standards.
The unregistered certificate anomaly and forensic QA
A certificate can exist with no registry entry. One talent had a signed passport, PDF, C2PA data and an OpenTimestamps receipt, and was live on the site, while the registry check failed on all three tiers. An unregistered certificate cannot be verified independently, so we read every line of the verify output, not the exit code.
This discrepancy revealed a critical gap between local asset generation and public ledger synchronization. During an internal audit, our team discovered an asset that appeared completely certified on disk—boasting signed PDFs, C2PA embeds, and timestamp receipts—yet returned immediate failures when queried against our public registry endpoint.
Because third-party brand auditors rely on public verification pages to confirm talent authenticity, an unindexed record renders all local cryptography commercially useless. Our deployment pipelines now mandate comprehensive end-to-end registry validation, reading every line of stdout to verify registry synchronization before approving talent distribution.
Discrepancies between local asset files and public registry indexes undermine external verification. If a client or auditor cannot independently validate a talent passport on our live verify endpoint, the certificate loses its practical commercial value. Our studio deployment protocols mandate automated line-by-line verification to ensure complete ledger synchronization prior to project signoff.
Chain integrity, re-issuance rules, and signer boundaries
Replacing or renaming a certified talent's WebP breaks the certificate, because the asset hash covers the listed files by name. A changed image requires re-issue. Tampering with any certified file breaks the chain root, which we demonstrated with a test.
Re-issuing a passport rebuilds it from scratch and wipes the Bitcoin anchor field, so the anchor is written after issuing, never before.
Because the re-issuance pipeline reconstructs the complete passport JSON structure, any existing blockchain receipt data is overwritten during rebuild. Anchoring must always occur as the absolute final step in the certification sequence, once all assets, registry entries, and hashes are permanently locked.
Limit: the C2PA embed is signed with the open-source tool's built-in test certificate. The certificate ID and chain root still embed and read back correctly, but a CA-trusted signer is a configuration change we have not made. Say so if a client asks.
Maintaining strict factual boundaries regarding our cryptographic signing infrastructure ensures enterprise clients understand exactly what our verification proves and where institutional trust boundaries reside.
In practical studio operations, combining multi-layer cryptographic hashing with public ledger verification gives commercial brands verifiable proof of talent uniqueness. Every certificate acts as a permanent technical record of generative craft.