
C2PA Content Credentials for Synthetic Models
How OMNI Labs embeds and verifies C2PA credentials using the open-source CLI: signed manifests, test signers, and what breaks verification.
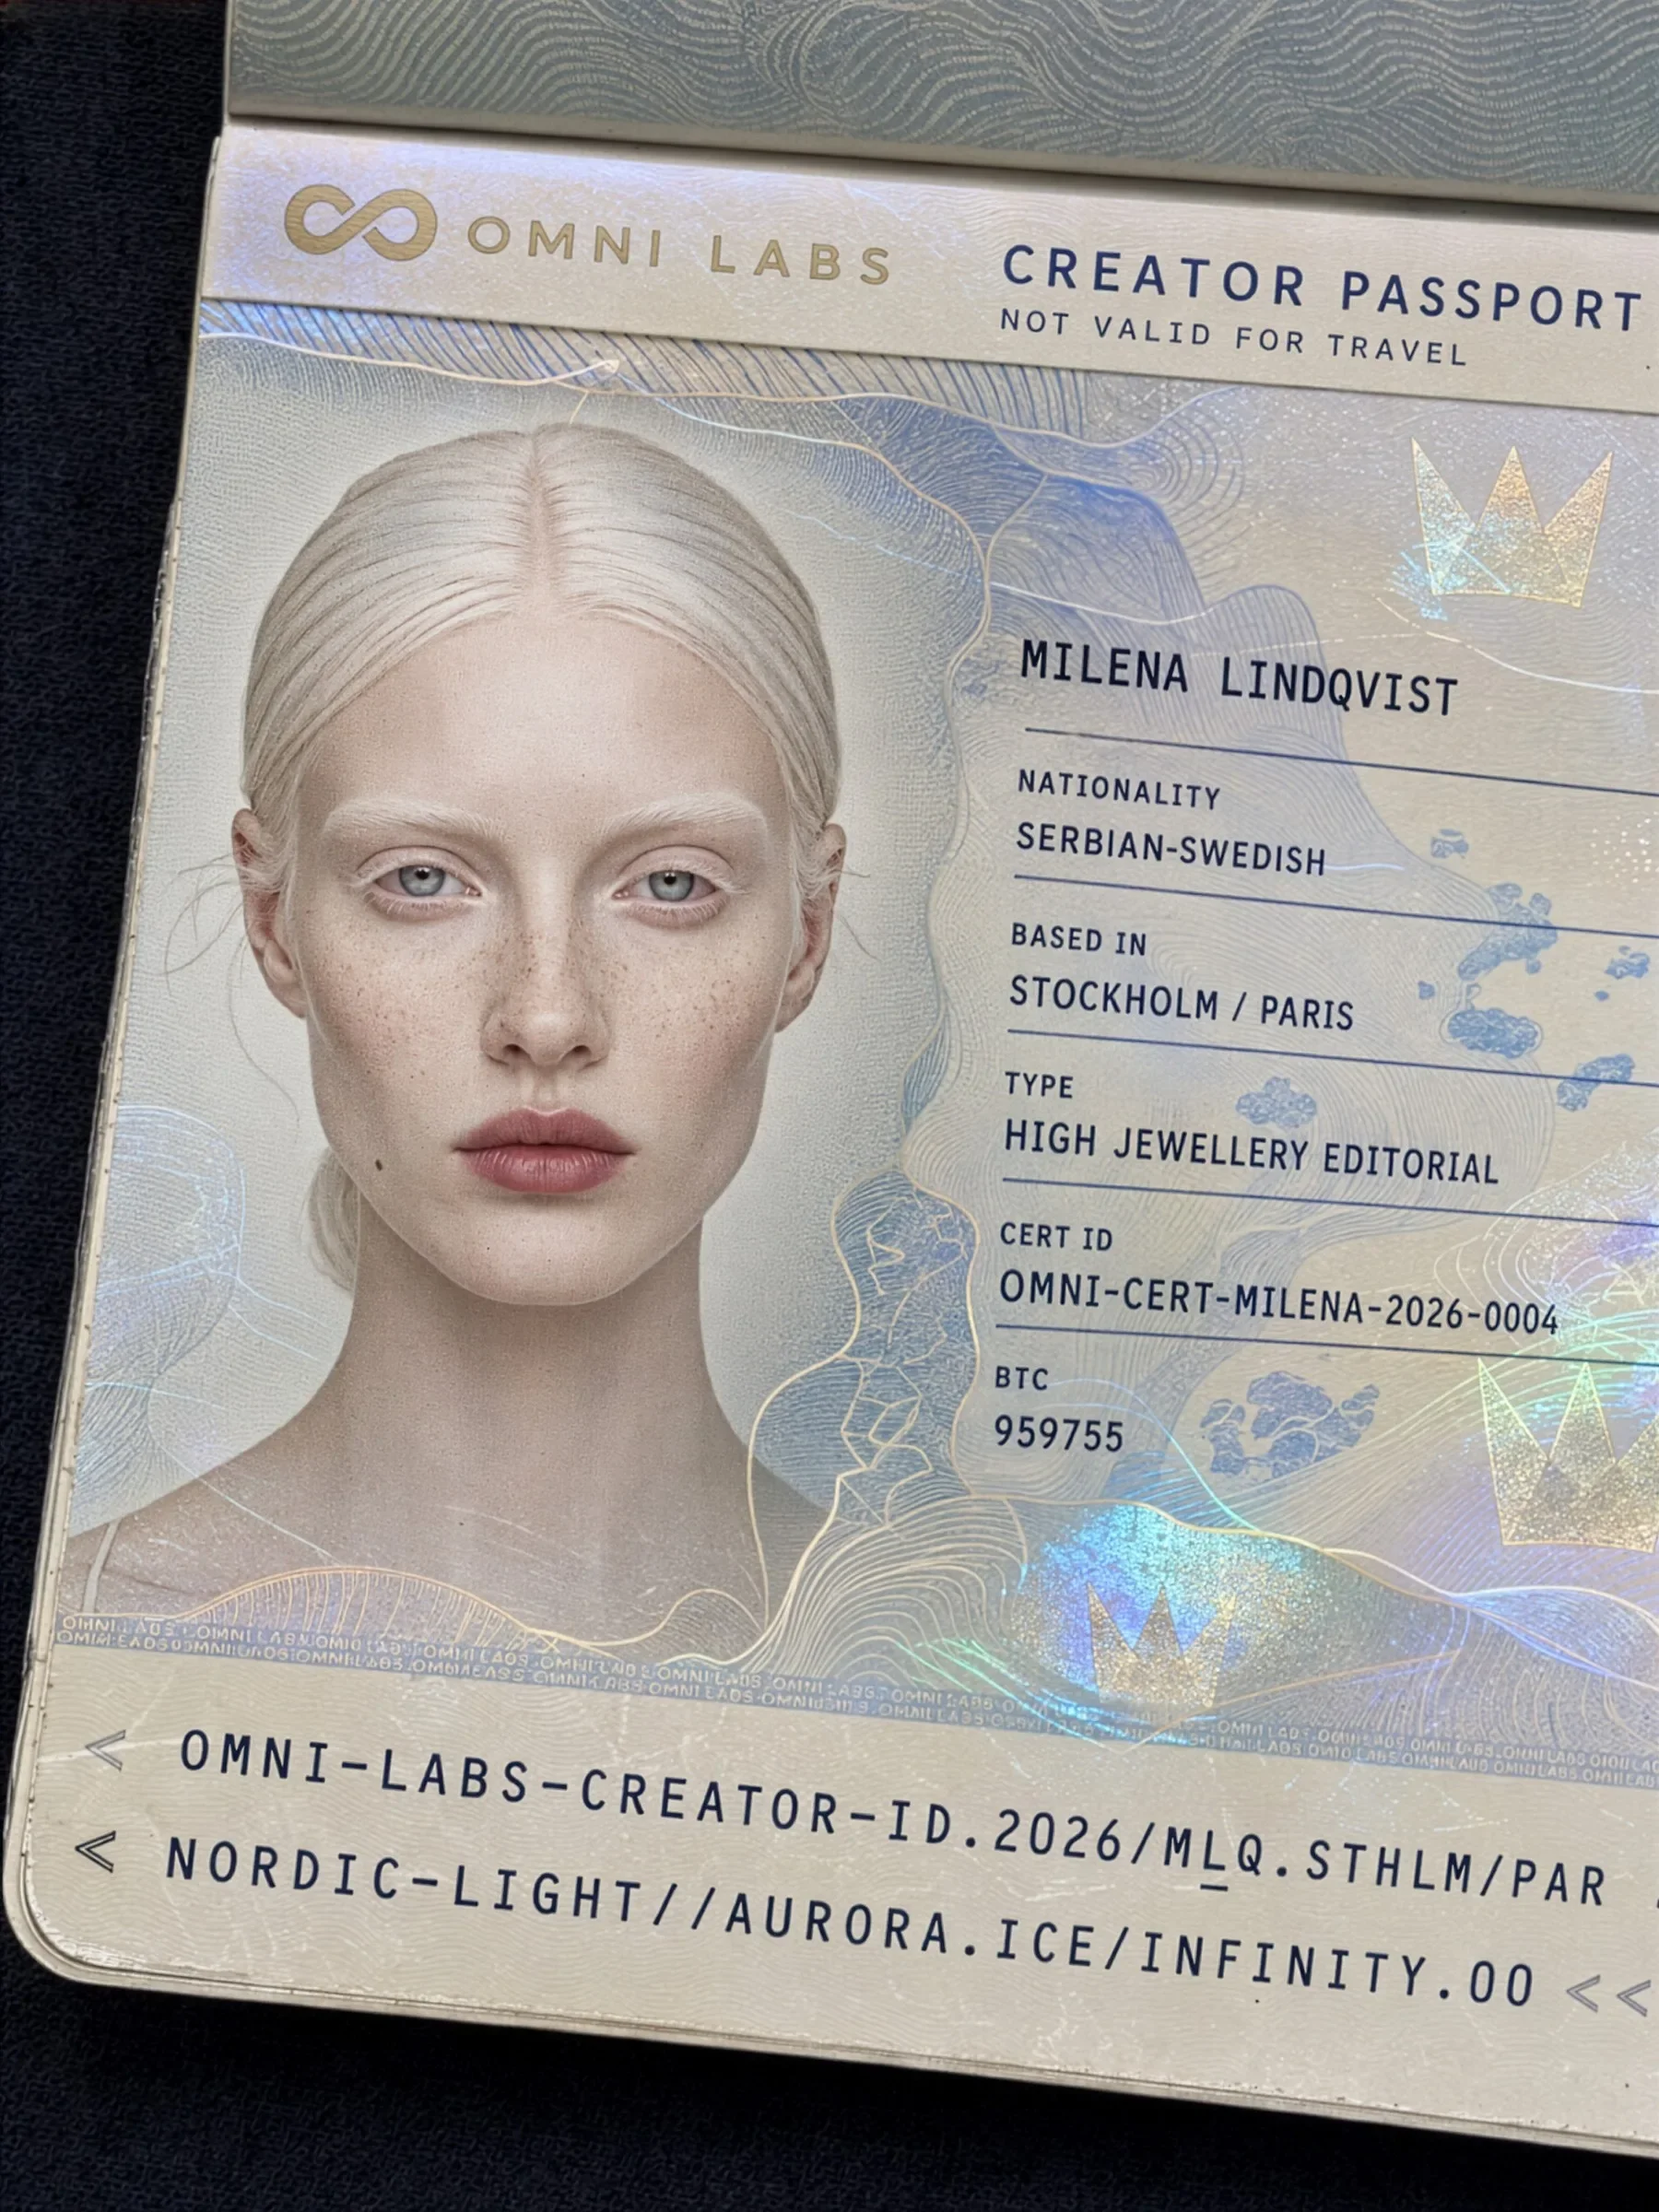
Key takeaways
- C2PA metadata is embedded exclusively on Verified and Enterprise tier certificates, omitting Basic records.
- OMNI Labs utilizes the open-source C2PA CLI version 0.26.67, bundled locally rather than from Windows package managers.
- Embedded claims declare synthetic: true and depicts_real_person: false alongside certificate IDs and lineage roots.
- The embedded signature currently relies on the tool's built-in test certificate rather than a commercial CA signer.
- Any modification or renaming of certified WebP image files breaks asset hash binding and invalidates the chain root.
C2PA credential architecture across certificate tiers
C2PA content credentials are embedded on the Verified and Enterprise certificate tiers, not on Basic.
In our studio certification infrastructure, cryptographic provenance serves as the primary barrier against synthetic asset tampering and fraudulent attribution. Basic certification establishes an identity record within our internal registry, but does not inject metadata directly into binary image files. By restricting C2PA packaging to our higher tiers, we ensure that commercial assets delivered to enterprise clients carry immutable provenance manifests embedded directly within their pixel headers.
We embed them with the open-source C2PA command-line tool, version 0.26.67, bundled locally. The tool is not on the Windows package manager and must be downloaded from its release page.
Deploying external security tooling across automated production pipelines requires disciplined dependency management. Because c2patool 0.26.67 is omitted from standard Windows package managers like winget or Chocolatey, our build runners maintain a pinned binary release within our local tool tree. This local bundle guarantees that every asset injection command executes against an identical binary hash, avoiding unversioned upstream breakage.
In our studio certification infrastructure, cryptographic provenance serves as an operational foundation rather than a decorative badge. When enterprise brands license synthetic characters for multi-market campaigns, their compliance departments demand verifiable audit trails. By establishing clear tier boundaries early in the asset preparation phase, our production teams avoid ambiguous asset deliveries.
Manifest assertions and test signer boundaries
The embedded assertion carries the certificate ID, the lineage chain root, synthetic: true, depicts_real_person: false and the verify URL.
These assertion fields establish explicit machine-readable boundaries for enterprise compliance. Stating synthetic: true explicitly notifies automated platform moderation engines that the media was synthetically generated. Simultaneously, setting depicts_real_person: false provides crucial legal clarity, certifying that the subject does not impersonate living human individuals or infringe upon personal publicity rights. The lineage chain root anchors the exact generation prompts and input reference weights back to our cryptographic ledger.
The signer is the tool's built-in test certificate. The certificate ID and chain root still embed and read back, but a CA-issued signer is a configuration swap we have not made yet. We make that distinction when a client asks whether the signer is trusted.
Transparency regarding cryptographic signing authority is essential for commercial enterprise workflows. While our manifest data structures conform strictly to C2PA specifications, signing via the default test certificate means third-party software may flag the signature as self-signed. The certificate ID and lineage root remain fully verifiable against our public verify pages, but corporate legal teams requiring root-of-trust chaining through commercial Certificate Authorities must be informed of this boundary prior to campaign distribution.
Clear declaration of synthetic origin represents best practice under global digital media guidelines. When automated verification tools parse an image, the presence of unambiguous boolean assertions allows distribution networks to classify content instantly. Simultaneously, binding the lineage chain root back to our repository ensures that every published still can be cross-referenced against original generation logs.
Automated verification and terminal parsing caveats
Verification is read line by line. The verifier can exit non-zero because of a console glyph while every check passed, so we read the per-line PASS or FAIL.
Automated CI/CD validation scripts often rely naively on shell exit codes to gate asset deployment. During our integration tests on Windows workstations, the c2patool binary frequently returned an exit code of 1 due to font rasterization errors or console unicode glyph issues, even when the underlying cryptographic manifest verified successfully. Relying on process exit codes caused our build runner to reject perfectly valid certified deliverables.
| Certificate Tier | C2PA Metadata | Lineage Chain Root | Signer Type |
|---|---|---|---|
| Basic | None | digital signature root | None |
| Verified | Embedded | cryptographic multi-layer | Built-in test certificate |
| Enterprise | Embedded | cryptographic asset hash | Built-in test certificate |
Our verification runner parses stdout line by line, evaluating individual test conditions independently. The audit script inspects each assertion block for explicit PASS markers across digital signatures, certificate hashes, and lineage manifests. Only when a literal FAIL token appears in the console stream does the gate halt deployment.
In high-volume commercial production, automated verification gates cannot afford false positives generated by shell encoding quirks. By analyzing stdout output stream tokens directly, our verification scripts confirm that signature validation, manifest parsing, and asset hashing all succeed. This robust parsing layer maintains strict security standards without interrupting delivery pipelines.
Asset hash binding and chain breakage conditions
What breaks the binding: changing the WebP changes the bound asset hash, so the embed no longer matches the certified file. Any change to a certified file also breaks the chain root.
Cryptographic manifests bind directly to the byte structure of final output deliverables. In our asset pipeline, every certified roster model is represented by high-resolution WebP images. If a designer opens a certified WebP in Photoshop, alters a single pixel, or saves the file with different compression settings, the cryptographic hash of the binary file changes instantly. The embedded C2PA claim will detect the mismatch and declare the credential invalid.
Even non-visual alterations can break the verification chain. Renaming an asset file or modifying associated metadata files breaks the multi-layer chain root calculation. Once a talent asset is stamped and registered, it must remain entirely untouched. Any design revision, crop adjustment, or color grade requires issuing a completely new certificate with a fresh lineage chain root.
Platform auto-detection limits in video distribution
Platform caveat: generated video may carry no C2PA metadata at all, so we do not rely on platform auto-detection and set the AI label by hand.
While social platforms and publishing channels increasingly mandate transparency for synthetic media, automated platform ingestion remains fragmented and fragile. In our video production tests across commercial rails, video transcoding engines routinely strip EXIF, XMP, and C2PA binary data blocks during upload. A synthetic clip injected with valid C2PA metadata will frequently lose its digital headers after passing through platform compression.
Assuming that social platforms will read embedded credentials and apply synthetic labels automatically creates severe regulatory compliance risk. In studio operations, we maintain an absolute policy of manually toggling platform AI disclosure settings across all published content, regardless of embedded metadata.
Combining manual platform disclosures with immutable C2PA embeds gives production studios a layered compliance posture. The client receives mathematically verifiable asset provenance for audit records, while public distribution remains fully compliant with platform guidelines.